Tech riderRev. 4 Oct 2026
Fuzzilli
- 1Runs onLinux, Mac, self-hosted
- 2CostsFree plan
- 3Input generation methodsmutation, generation, hybrid
- 4Target typesJavaScript programs and JavaScript engines/interpreters
- 5Coverage guidanceYes
- 6Crash triageYes
- 7Execution modehybrid
- 8Supported languagesJavaScript
8 lines stated Written from the maker's own pages: github.com
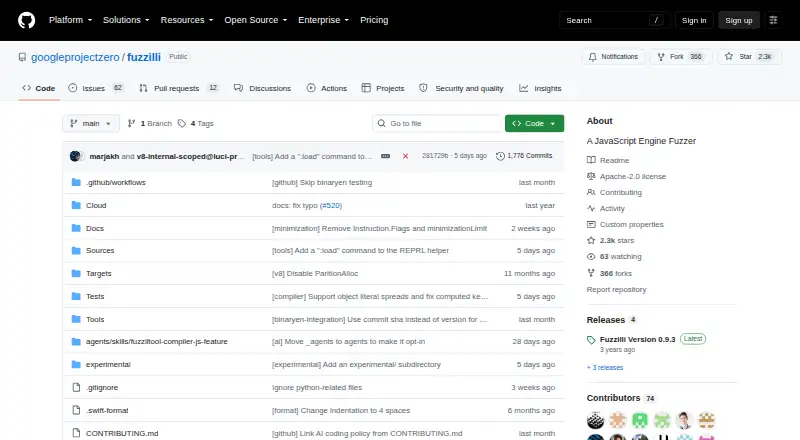
Overview
Fuzzilli is ranked #8 of 27 in fuzz testing software on Specifiction. It runs on Linux, macOS, Self-hosted. There is a free plan.
Fuzzilli plans and pricing
All plansFuzzilli Free Apache-2.0 licensed source code · requires building the fuzzer and a supported, instrumented JavaScript engine github.com · 4 Oct 2026
Compared on fuzz testing software
- Input generation methods
- mutation, generation, hybridgithub.com
- Target types
- JavaScript programs and JavaScript engines/interpretersgithub.com
- Coverage guidance
- Yesgithub.com
- Crash triage
- Yesgithub.com
- Execution mode
- hybridgithub.com
- Supported languages
- JavaScriptgithub.com
- CI/CD support
- Yesgithub.com
Facts
- What it does
- Fuzzilli is a coverage-guided fuzzer for dynamic language interpreters, built around a custom intermediate language called FuzzIL that can be mutated and translated to JavaScript.github.com · 3 Oct 2026
- Mutations
- Its documented mutators can change data flow, generate or splice code, combine corpus programs, and modify operation parameters.github.com · 3 Oct 2026
- Fuzzer components
- The listed components include a mutation fuzzer, script runner, corpus, environment, minimizer, evaluator, and lifter.github.com · 3 Oct 2026
- Execution
- Fuzzilli uses a read-eval-print-reset-loop mode in which a modified target engine accepts scripts over pipes or shared memory, executes them, resets, and waits for the next script.github.com · 3 Oct 2026
- Scaling
- Multiple instances can synchronize within one process or over a TCP-based protocol, allowing scaling across cores and machines.github.com · 3 Oct 2026
- Supported targets
- The repository lists JavaScriptCore, JerryScript, QuickJS, QtJS, Serenity, SpiderMonkey, V8, XS, Duktape, and njs target directories.github.com · 3 Oct 2026
- Build requirements
- The usage instructions call for compiling a supported JavaScript engine with coverage instrumentation using clang 4.0 or later, then building Fuzzilli with Swift Package Manager.github.com · 3 Oct 2026
- Deployment
- The project says Fuzzilli and supported engines can be built and run inside Docker and on Google Compute Engine.github.com · 3 Oct 2026
- Cloud tooling
- Its Cloud directory contains Docker scripts and files, Google Compute Engine setup and teardown scripts, and rudimentary crash triaging.github.com · 3 Oct 2026
- Security results
- The repository’s bug showcase lists security issues found with Fuzzilli across engines including WebKit/JavaScriptCore, SpiderMonkey, V8, Duktape, JerryScript, and Hermes.github.com · 3 Oct 2026
- Security disclosure
- The project asks users to send a short note, possibly with a CVE number, or open a pull request to have a vulnerability found with Fuzzilli considered for the bug showcase.github.com · 3 Oct 2026
- License
- The repository identifies its license as Apache-2.0.github.com · 3 Oct 2026
- Support status
- The repository states that Fuzzilli is not an officially supported Google product.github.com · 3 Oct 2026
- Intended users
- The project describes Fuzzilli as a tool for fuzzing dynamic language interpreters and invites patches and other contributions.github.com · 3 Oct 2026
- Purpose
- Fuzzilli is a coverage-guided fuzzer for dynamic language interpreters that mutates programs in FuzzIL and translates them to JavaScript.github.com · 4 Oct 2026
- Mutation
- Its mutators change program data flow, generate or splice code, combine corpus programs, and alter operation parameters.github.com · 4 Oct 2026
- Core components
- The fuzzer includes a mutation fuzzer, script runner, corpus, runtime environment, minimizer, evaluator, and lifter.github.com · 4 Oct 2026
- Distributed fuzzing
- Multiple instances can synchronize over a TCP-based protocol across machines or through dispatch queues within one process.github.com · 4 Oct 2026
- Cloud deployment
- The project provides Docker scripts and files for local or distributed fuzzing and scripts for setting up and tearing down distributed fuzzing on Google Compute Engine.github.com · 4 Oct 2026
- Security findings
- The repository’s bug showcase lists security-impacting bugs found with Fuzzilli in JavaScript engines including WebKit, SpiderMonkey, V8, Duktape, JerryScript, and Hermes.github.com · 4 Oct 2026
- Google support
- The repository states that Fuzzilli is not an officially supported Google product.github.com · 4 Oct 2026
- Contributions
- Project contributions require a Contributor License Agreement and are reviewed through GitHub pull requests.github.com · 4 Oct 2026
Best Fuzzilli alternatives
See all 20 All accessCh 01 Mayhem Free planFree trialAPI from $236/mo7.8 All accessCh 02 ClusterFuzz Free planLinuxMac Free to start7.6 All accessCh 03 AFL++ Free planAndroidLinux from €1666.67/mo7.5 All accessCh 04 cargo-fuzz Free planLinuxMac Free to start7.5 All accessCh 05 Accessibility Test Framework for Android Free planAndroidLinux Free to start7.3 All accessCh 06 Jazzer Free planLinuxMac Free to start7.2

Where it ranks on Specifiction
Is Fuzzilli yours?
Claim it for free: prove the domain, then correct facts, plans and screenshots. An editor reviews every change.
Sources
- github.com/googleprojectzero/fuzzilli· checked 3 Oct 2026
- github.com/googleprojectzero/fuzzilli/tree/main/Ta· checked 3 Oct 2026
- github.com/googleprojectzero/fuzzilli/tree/main/Cl· checked 3 Oct 2026
- github.com/googleprojectzero/fuzzilli/blob/main/CO· checked 4 Oct 2026