Intruder
Vulnerability Scanning Software
Overview
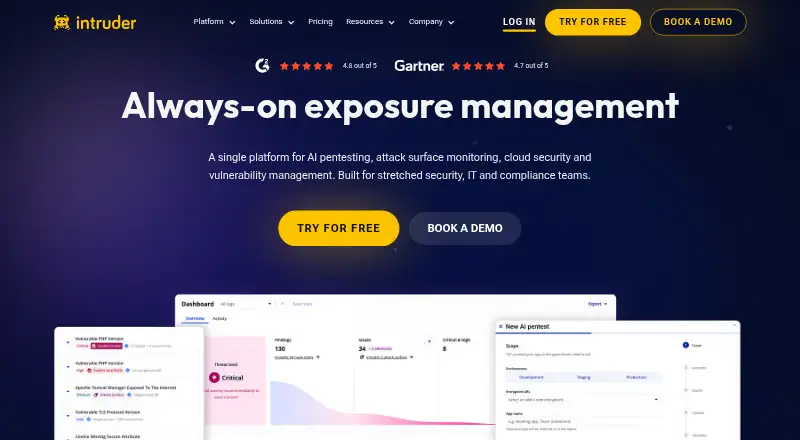
Intruder provides continuous vulnerability scanning for infrastructure, web applications, APIs, and cloud environments, with issue prioritization and remediation guidance. It ranks issues using exploit likelihood and real-world threat intelligence, while emerging-threat scans check systems within hours of new risks appearing. Cloud scans assess AWS, Microsoft Azure, and Google Cloud environments for vulnerabilities, misconfigurations, and exposures. Authenticated dynamic application testing covers customer-controlled web apps and APIs, including OWASP Top 10 checks. Supported targets also include external IP addresses, domains, subdomains, internal Windows, macOS, and Linux devices, and container images. Integrations include cloud platforms, code hosts, issue trackers, chat services, Vanta, and Drata. Its API can manage targets, view issues, start scans, and retrieve results. A free plan and 14-day trial are listed. The free plan covers five infrastructure targets and weekly external scans, but does not include web apps. Internal target scanning is available only on Pro and Enterprise plans. All customers receive live chat support.
Who it is for
Intruder suits teams responsible for finding and prioritizing vulnerabilities across infrastructure, cloud environments, web apps, or APIs. Its free tier may fit users scanning a small number of infrastructure targets without web app coverage.
What is good
- Checks for emerging risks within hours.
- Scans AWS, Azure, and Google Cloud environments.
- Includes authenticated web app and API testing.
- All customers receive live chat support.
What to know first
- Free plan excludes web apps.
- Free plan covers five infrastructure targets.
- Internal target scanning requires Pro or Enterprise.
Specifiction review
Intruder: the full review
Intruder combines continuous scanning with prioritization and remediation guidance across a wide range of target types. The free plan is limited, and internal scanning requires a higher-tier plan.
Overview
Intruder is a vulnerability-scanning service for teams responsible for exposed infrastructure, applications and cloud environments. It suits security and IT teams that need ongoing coverage across several target types and help deciding which findings deserve attention. Its breadth and risk-based prioritization are compelling; the free plan is narrow, and internal scanning starts at Pro.
Key features
Continuous scanning and response
Intruder continuously scans infrastructure, web apps and APIs, then ranks issues by exploit likelihood and real-world threat intelligence. That makes the output more actionable than an undifferentiated list, particularly for teams facing a large backlog. Remediation guidance helps carry findings toward action, though prioritization does not remove the work of resolving them.
Emerging-threat scans check systems within hours of new risks appearing in the wild. This is useful for teams that need to reassess exposure as threats emerge, alongside routine scans.
Coverage across applications, cloud and devices
Authenticated dynamic testing covers customer-controlled web applications and APIs, including OWASP Top 10 checks. Cloud scans assess AWS, Microsoft Azure and Google Cloud for vulnerabilities, misconfigurations and exposures. Supported targets also include external addresses and domains, internal Windows, macOS and Linux devices, and container images. The range is a strength for teams seeking one scanning service across mixed environments, but the plan boundaries matter: internal target scanning is restricted to Pro and Enterprise.
Integrations include AWS, Azure, Google Cloud, GitHub, GitLab, Jira, Linear, ServiceNow, Slack, Microsoft Teams, Vanta and Drata. Its API can manage targets, view issues, start scans and retrieve results, giving teams options to connect scanning to existing workflows.
Security and support
Intruder says it encrypts data in transit with TLS, separates client datasets logically, and uses full-disk encryption on company devices and cloud volumes storing customer information. Intruder Systems Ltd says it completed an AICPA SOC 2 Type 2 audit. The company cites SOC 2, ISO 27001, PCI DSS, HIPAA and Cyber Essentials among supported compliance frameworks. All customers receive live chat support; Enterprise adds access to dedicated security professionals.
Pricing
Intruder is freemium, with a free plan and a 14-day trial. Paid-plan prices are custom pricing or based on a base fee plus per-target charges, so the free tier is the only stated fixed price.
| Plan | Price and terms | What it includes |
|---|---|---|
| Free | 0.00 USD per free, billed Forever | 5 infrastructure targets, weekly external scans, 1 connected cloud account, 2 container images, ports 80 and 443, and 3 users. Web apps are excluded. |
| Cloud | Custom pricing; billed Monthly or annually (annual saves 20%); base fee plus per-target fee | 3 cloud accounts, daily cloud checks, web app and API testing, top 10 ports, 5 AI investigation credits and 15+ integrations. |
| Pro | Custom pricing; billed Annually; base fee plus per-target fee | 10 cloud accounts, agent-based internal scanning, top 50 ports and 10 AI investigation credits. |
| Enterprise | Custom pricing; billed Quoted separately | Unlimited cloud accounts, all ports, 1,000+ attack surface checks, 50 AI investigation credits and shadow IT discovery. |
Free is suited to small external-infrastructure inventories, but its five-target cap, narrow port coverage, weekly cadence and three-user ceiling limit its value for broader programs. Cloud adds application testing and more frequent cloud checks, but does not include the internal scanning explicitly offered by Pro. Pro is the relevant step for agent-based internal scanning and broader port coverage; Enterprise is aimed at organizations needing extensive attack-surface checks and unlimited cloud accounts. Live chat is available across plans, while dedicated security professionals are an Enterprise benefit.
Platforms
Intruder supports API, Linux, macOS, web and Windows. Its deployment model is hybrid, and authenticated scanning is supported.
Who it's for
Intruder is a good fit for teams that want continuous vulnerability coverage spanning infrastructure, cloud and customer-controlled applications, with threat-informed prioritization to help focus remediation. It is less suitable for a team that needs internal scanning but cannot take on Pro's custom-priced, annually billed base-fee-plus-target model, or for a small user group whose needs exceed the free tier's caps.
Pros and cons
- Pro: Broad target coverage includes cloud environments, APIs, web apps, internal devices and container images, reducing the need to treat each asset type as a separate scanning problem.
- Pro: Exploit-likelihood and threat-intelligence prioritization, plus remediation guidance, helps teams focus effort on more urgent findings.
- Pro: Emerging-threat checks run within hours of new risks appearing, complementing continuous scanning.
- Con: The free plan excludes web apps and limits users, targets, scan frequency, cloud accounts and ports, so it is a constrained evaluation option rather than broad coverage.
- Con: Internal target scanning is reserved for Pro and Enterprise, and paid pricing uses custom or base-fee-plus-target terms rather than a stated flat price.
Alternatives
For a different vulnerability-management option, consider ManageEngine Vulnerability Manager Plus; its free edition and listed Professional on-premises option make it worth comparing if those licensing and deployment choices matter. OpenVAS is another freemium alternative, with a free virtual appliance, community feed and limited enterprise features, but no default support on its free plan. Choose Nmap when a free end-user-licensed tool is the priority and its redistribution restriction is acceptable; its stated scope is a network scanner rather than Intruder's continuous, prioritized service.
Qualys External Attack Surface Management is a candidate for readers who want to try a 30-day no-cost CSAM with EASM offer, rather than Intruder's permanently free but capped tier. Nuclei suits readers seeking an open-source, MIT-licensed standalone CLI. Pentest-Tools Port Scanner is a narrower port-scanning alternative, with a free tier for open ports and services discovery. Ivanti Neurons for Zero Trust Access is an alternative for readers considering named-user-licensed SaaS access software. NSAuditor AI is another freemium network vulnerability-scanning option.
Compare broader categories in Vulnerability Scanning Software, Cloud Vulnerability Scanners, Network Vulnerability Scanners and Vulnerability Management Software.
Verdict
Choose Intruder if your team needs continuous scanning across infrastructure, cloud and applications, and values threat-informed prioritization and remediation guidance. Its broad coverage is the main reason to choose it; the limited free tier and the higher-tier gate on internal scanning are the main reasons to look elsewhere.
Intruder plans and pricing
All plansCompared on vulnerability scanning software
- Free plan
- Yesintruder.io
- Deployment model
- hybridintruder.io
Facts
- Product
- Intruder provides continuous vulnerability scanning for infrastructure, web apps, and APIs, with prioritization and remediation guidance.intruder.io · 30 Sept 2026
- Emerging threats
- Emerging threat scans check systems within hours of new risks appearing in the wild.intruder.io · 30 Sept 2026
- Prioritization
- Intruder prioritizes issues using exploit likelihood and real-world threat intelligence.intruder.io · 30 Sept 2026
- Cloud security
- Cloud security scans assess AWS, Microsoft Azure, and Google Cloud environments for vulnerabilities, misconfigurations, and exposures.help.intruder.io · 30 Sept 2026
- App scanning
- Authenticated dynamic application security testing covers web apps and APIs controlled by the customer, including OWASP Top 10 checks.intruder.io · 30 Sept 2026
- Integrations
- Listed integrations include AWS, Azure, Google Cloud, GitHub, GitLab, Jira, Linear, ServiceNow, Slack, Microsoft Teams, Vanta, and Drata.help.intruder.io · 30 Sept 2026
- API
- Intruder's API can manage targets, view issues, start scans, and retrieve results.help.intruder.io · 30 Sept 2026
- Security
- Intruder says it uses TLS encryption for data in transit, logical data separation between client datasets, and full-disk encryption on company devices and cloud volumes storing customer information.intruder.io · 30 Sept 2026
- Compliance
- Intruder Systems Ltd says it successfully completed an AICPA SOC 2 Type 2 audit.intruder.io · 30 Sept 2026
- Support
- All customers receive live chat support, and Enterprise customers also have access to dedicated security professionals.intruder.io · 30 Sept 2026
- Limits
- Internal target scanning is available only on Pro and Enterprise plans.intruder.io · 30 Sept 2026
- Company
- Intruder says it was founded in 2015 to address information overload in vulnerability management.intruder.io · 30 Sept 2026
Best Intruder alternatives
See all 12
 $57.92/mo7.8 OpenVAS Free plan apiLinuxMacself-hostedWeb

 €210.33/mo7.8 Nmap Free plan LinuxMacself-hostedWin
 $9,980/mo7.7 Qualys External Attack Surface Management Free trial apiLinuxWeb
 7.5 Nuclei Free plan LinuxMacself-hostedWin
 Free7.4 Pentest-Tools Port Scanner Free plan apiWeb
 $95/mo7.4
Where it ranks on Specifiction
Is Intruder yours?
Claim it for free: prove the domain, then correct facts, plans and screenshots. An editor reviews every change.
Sources
- intruder.io/platform/vulnerability-management· checked 30 Sept 2026
- help.intruder.io/en/articles/13129434-cloud-security-sca· checked 30 Sept 2026
- intruder.io/pricing· checked 30 Sept 2026
- help.intruder.io/en/collections/2770155-integrations· checked 30 Sept 2026
- intruder.io/security· checked 30 Sept 2026
- intruder.io/about-us· checked 30 Sept 2026