Tech riderRev. 4 Oct 2026
- 1Runs onLinux
- 2CostsFree plan
- 3Prompt injection testsYes
- 4Jailbreak testsYes
- 5Data leakage testsYes
- 6Deployment modeself hosted
6 lines stated Written from the maker's own pages: github.com
Overview
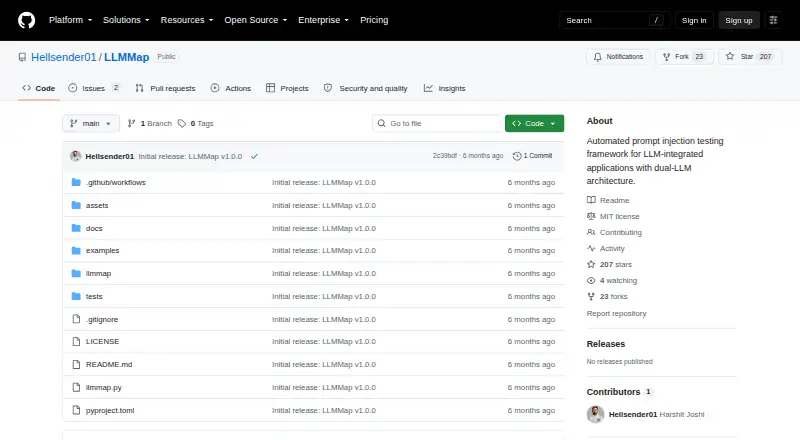
LLMMap is ranked #28 of 29 in AI security testing tools on Specifiction. It runs on Linux. There is a free plan.
LLMMap plans and pricing
All plansLLMMap Free No charge stated; publicly available under the MIT license. Python >= 3.11 · Requires an LLM backend; Ollama is local, while cloud backends may require API keys github.com · 4 Oct 2026
Compared on AI security testing tools
- Prompt injection tests
- Yesgithub.com
- Jailbreak tests
- Yesgithub.com
- Data leakage tests
- Yesgithub.com
- Deployment mode
- self_hostedgithub.com
Facts
- Purpose
- LLMMap tests LLM-integrated applications for prompt injection by discovering HTTP injection points, generating targeted prompts, and checking findings for reliability.github.com · 4 Oct 2026
- Prompt coverage
- It includes 227 prompt injection techniques across 18 attack families in four prompt packs.github.com · 4 Oct 2026
- Detection
- A Generator LLM creates goal-aware prompts and a Judge evaluates target responses; detector signals can include heuristics and optional semantic similarity.github.com · 4 Oct 2026
- Supported LLMs
- The documented backends are Ollama, OpenAI, Anthropic, and Google, with Ollama as the local default that needs no API key.github.com · 4 Oct 2026
- Request input
- Targets can be supplied as a URL or a Burp Suite request export, with an asterisk marking an injection location.github.com · 4 Oct 2026
- Burp Suite
- LLMMap reads Burp Suite request exports natively and lists proxy support for traffic inspection.github.com · 4 Oct 2026
- Injection locations
- It supports injection in query parameters, request bodies, headers, cookies, and paths.github.com · 4 Oct 2026
- Obfuscation
- Its listed obfuscation methods include base64, homoglyphs, leet speak, and language switching.github.com · 4 Oct 2026
- Reliability
- Candidate findings are re-tested using Wilson confidence intervals; the documented defaults are five retries and three confirmations.github.com · 4 Oct 2026
- Safety
- Safe mode is enabled by default and restricts scans to low-risk prompt families, while risky families such as tool abuse and system override are blocked.github.com · 4 Oct 2026
- Data handling
- Scan workspaces store request metadata, configuration, and timing; sensitive prompt text and response bodies stay in memory and are not written to disk by default.github.com · 4 Oct 2026
- Dry run
- Dry-run mode plans a scan and selects prompts without making network connections to the target.github.com · 4 Oct 2026
- Notable limits
- The architecture document says adaptive TAP and out-of-band detection modules are reserved for future versions and inactive in the v1.0.0 scan pipeline.github.com · 4 Oct 2026
- Intended users
- The project describes LLMMap as a security testing tool for authorized use and says to test only systems owned by the user or covered by explicit written authorization.github.com · 4 Oct 2026
Best LLMMap alternatives
See all 12 All accessCh 01 F5 BIG-IP APM Free trialAndroidAPI 7.7 All accessCh 02 OpenSecureAI Scanner Free planAPILinux from $49/mo7.4 All accessCh 03 Project Moonshot Free planAPILinux Free to start7.4 All accessCh 04 AIRTA Red Team Free planAPILinux Free to start7.3 All accessCh 05 Promptfoo Free planAPILinux Free to start7.3 All accessCh 06 PromptGuard Free planAPIBrowser from $19/mo7.3

Where it ranks on Specifiction
Is LLMMap yours?
Claim it for free: prove the domain, then correct facts, plans and screenshots. An editor reviews every change.
Sources
- github.com/Hellsender01/LLMMap· checked 4 Oct 2026
- github.com/Hellsender01/LLMMap/blob/main/docs/ARCH· checked 4 Oct 2026
- github.com/Hellsender01/LLMMap/blob/main/docs/AUTH· checked 4 Oct 2026