- 1Runs onAndroid, Linux, Mac, Windows
- 2CostsFree plan
- 3Live captureYes
- 4Offline trace analysisYes
- 5Display filtersYes
- 6Capture file formatspcap
- 7Command-line captureYes
- 8Supported platformsLinux, macOS, BSD variants, Android (Termux), Windows
Overview
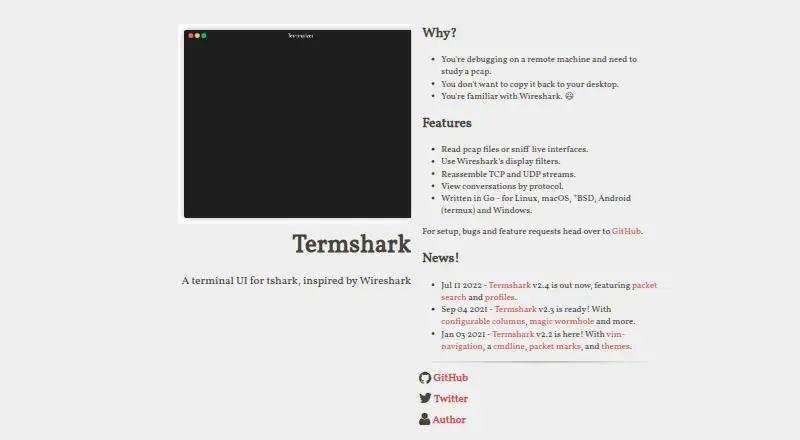
Termshark is a terminal interface for tshark, inspired by Wireshark, for inspecting saved packet captures and live network traffic. It can read pcap files and sniff live interfaces when tshark permits, then apply Wireshark display filters to either. Users can inspect and reassemble TCP and UDP flows, search packets, copy packet ranges, and view conversations involving Ethernet, IPv4, IPv6, UDP, and TCP. Version 2.4 added packet search and profiles for colors and columns. It supports 16-color, 256-color, and truecolor terminal modes. The project lists Linux, macOS, BSD variants, Android through Termux, and Windows, with precompiled executables available through GitHub releases. Termshark is aimed at remote debugging where a large capture can be examined on the remote machine rather than copied to a desktop. It is free and MIT licensed. Packet analysis requires tshark 1.10.2 or newer in PATH; the project notes that tshark has features Termshark does not expose.
Who it is for
Termshark suits people debugging on remote machines who need to examine pcaps without copying them to a desktop. It can also serve users who want terminal-based inspection of saved captures or live traffic.
What is good
- Reads pcap files and sniffs live interfaces.
- Supports Wireshark display filters.
- Reassembles and inspects TCP and UDP flows.
- Available for Linux, macOS, BSD, Android, and Windows.
- Free under the MIT license.
What to know first
- Requires tshark 1.10.2 or newer in PATH.
- Some tshark features are not exposed.
- Live sniffing depends on tshark permission.
Verdict
Termshark provides packet inspection and filtering in a terminal, including for remote captures. It is free, but requires a compatible tshark installation and exposes less functionality than tshark itself.
Termshark plans and pricing
All plansCompared on network packet capture software
- Free plan
- Yestermshark.io
- Live capture
- Yestermshark.io
- Offline trace analysis
- Yestermshark.io
- Display filters
- Yestermshark.io
- Capture file formats
- pcaptermshark.io
- Command-line capture
- Yestermshark.io
- Supported platforms
- Linux, macOS, BSD variants, Android (Termux), Windowstermshark.io
Facts
- Purpose
- Termshark is a terminal user interface for tshark, inspired by Wireshark.termshark.io · 30 Sept 2026
- Use case
- The project describes using Termshark to inspect a large pcap on a remote machine without copying it to a desktop.github.com · 30 Sept 2026
- Capture and files
- Termshark can read pcap files and sniff live interfaces when tshark is permitted.github.com · 30 Sept 2026
- Filters
- It filters pcaps and live captures using Wireshark display filters.github.com · 30 Sept 2026
- Stream analysis
- It can reassemble and inspect TCP and UDP flows.github.com · 30 Sept 2026
- Conversations
- Its conversation view currently supports Ethernet, IPv4, IPv6, UDP, and TCP.github.com · 30 Sept 2026
- Packet search
- The project homepage lists packet search among the features introduced in version 2.4.termshark.io · 30 Sept 2026
- Profiles
- The homepage says version 2.4 includes profiles for colors and columns.termshark.io · 30 Sept 2026
- Runtime dependency
- Termshark requires tshark version 1.10.2 or higher in the PATH for packet analysis.github.com · 30 Sept 2026
- Platform support
- The project lists downloads for Linux, macOS, BSD variants, Android through Termux, and Windows.github.com · 30 Sept 2026
- Downloads
- Precompiled executables are available through the project's GitHub releases.github.com · 30 Sept 2026
- Support
- The homepage directs users to GitHub for setup, bugs, and feature requests.termshark.io · 30 Sept 2026
- License
- The GitHub repository identifies the project as MIT licensed.github.com · 30 Sept 2026
- Limit
- The project notes that tshark has more features than Termshark currently exposes.github.com · 30 Sept 2026
- Packet files
- It reads pcap files and can sniff live interfaces.termshark.io · 30 Sept 2026
- Filtering
- It supports Wireshark display filters for pcap files and live captures.github.com · 30 Sept 2026
- Packet copying
- It can copy ranges of packets to the clipboard from the terminal.github.com · 30 Sept 2026
- Search and profiles
- Version 2.4 added packet search and profiles for colors and columns.termshark.io · 30 Sept 2026
- Terminal support
- The program supports 16-color, 256-color and truecolor terminal modes.github.com · 30 Sept 2026
- Dependencies
- Termshark depends on tshark, tcell and gowid, and tshark must be available in PATH.github.com · 30 Sept 2026
- Resource use
- The user guide says loaded packet data uses approximately 10 MB of RAM per 1,000 packets.github.com · 30 Sept 2026
- Target users
- The project is aimed at people debugging on remote machines who need to study pcaps without copying them to a desktop.termshark.io · 30 Sept 2026
Best Termshark alternatives
See all 19

Where it ranks on Specifiction
Is Termshark yours?
Claim it for free: prove the domain, then correct facts, plans and screenshots. An editor reviews every change.
Sources
- termshark.io· checked 30 Sept 2026
- github.com/gcla/termshark/· checked 30 Sept 2026
- github.com/gcla/termshark/blob/master/docs/UserGui· checked 30 Sept 2026
- github.com/gcla/termshark· checked 30 Sept 2026